Ukraine Sensor — Final Statistics
This passive honeypot sensor in Ukraine has been decommissioned. The live feed is gone; the figures below are a frozen snapshot generated 2026-10-12 13:42 UTC from everything it recorded. Collection ran from 2026-08-30 20:19:01 to 2026-10-02 21:10:14 UTC.
Totals
| Attacker interactions (emulated services) | 4,454,973 |
| Unique source IPs | 7,222 |
| Source networks (ASNs) / countries | 1,580 / 145 |
| Connection attempts dropped on unemulated ports | 621,070 |
| Passive TCP/IP fingerprint records (p0f) | 6,082,386 |
| IOC matches (ThreatFox C2/botnet IP list, 2,612 rows) | 0 of 7,222 sources |
Patterns observed
- Ramp, peak, then plateau. Daily volume climbed from about 600 interactions on day one to a peak of 615,277 on 2026-09-10. It eased to 173K–268K per day over 09-12 to 09-15, then held at 101K–138K per day from 09-16 to 09-22, with roughly 900–1,000 distinct sources per day.
- VNC dominated. Port 5900 (VNC) accounted for about 86% of all interactions (3.85M), from 777 sources. SSH was second (357K, 3,814 sources), then MySQL (198K) and Telnet (31K).
- No day/night cycle. Hourly volume stayed within about 165K–202K per hour bucket across all 24 UTC hours. That flatness points to automated, always-on scanning rather than operators working a schedule.
- Hosting providers did most of the work. DigitalOcean, Contabo and Dynu together produced roughly two-thirds of all interactions. The top single source (AS213790) is a UK-registered network whose addresses geolocate to Germany.
- Coordinated bursts. Four Dynu-hosted addresses (AS398019) each logged about 57K–59K hits, all with last-seen times within the same three seconds on 2026-09-11, which is consistent with one scanning campaign spread across several addresses.
- Persistent sources. Several addresses were still active on the last day of data (2026-10-02), including the single most active source, so the scanning was ongoing rather than a one-off surge.
- Scanning is geographically broad. The United States, Germany and China were the top source countries by hits, but traffic came from 145 countries.
- TCP fingerprints. About half of the fingerprinted SYN packets matched Linux 2.2.x–3.x stacks and about 13% matched Windows 7/8. About 29% matched no known signature.
- Common targets beyond the emulated services. Dropped connection attempts clustered on port 2222 (alternate SSH), 3389 (RDP), 8443, 8000, 554 (RTSP), 53 (DNS) and 25 (SMTP).
Timeline
| Date (UTC) | What happened |
|---|---|
| 2026-08-30 | Sensor deployed; log pipeline to the collector went live. |
| 2026-08-31 – 09-10 | Volume ramp from about 16K to 615K interactions per day; distinct sources per day rose from 269 to 1,034. |
| 2026-09-01 | Passive TCP/IP fingerprinting (p0f) added. |
| 2026-09-11 | Coordinated Dynu-hosted burst (see patterns). |
| ~2026-09-13 | Log shipping for the emulated services stopped (a log-reader fault on the sensor, not a change in attacker activity). Most of the affected records were re-shipped and ingested on 09-30. |
| 2026-09-12 – 09-22 | Volume eased from the peak to a plateau: 173K–268K per day over 09-12 to 09-15, then 101K–138K per day from 09-16 to 09-22. |
| 2026-09-23 08:10 | Last report from the sensor before a hosting-facility outage. Several active sources were still mid-scan at that moment. |
| 2026-09-24 – 09-28 | Sensor offline (outage at the hosting facility). No data recorded. |
| 2026-09-28 15:57 | Sensor back online. |
| 2026-09-30 | Log shipping repaired. The backlog for 09-13 through 09-23 was re-shipped and ingested that day, so most of those figures arrived in one batch. |
| 2026-10-02 21:10 | Last recorded interaction. |
| 2026-10-12 | Sensor decommissioned. This page is the final snapshot. |
Outage: September 2026
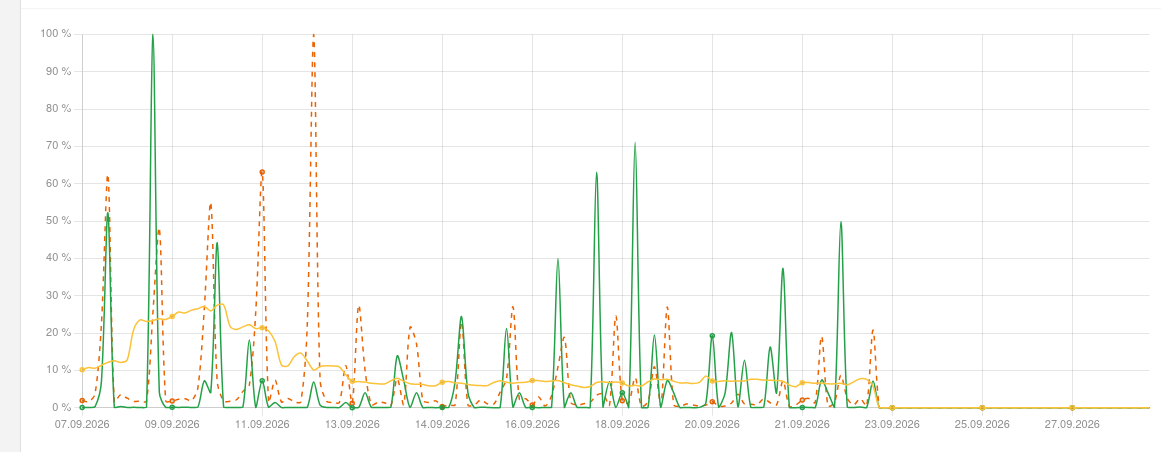
Daily interactions
Bars are interactions per day (UTC). Gaps are periods the sensor was offline or not reporting. Dates are the attacker-side timestamps.
| Date (UTC) | Interactions | Sources | Dropped connection attempts |
|---|---|---|---|
| 2026-08-30 | 590 | 52 | 1,540 |
| 2026-08-31 | 15,974 | 269 | 26,259 |
| 2026-09-01 | 42,081 | 289 | 17,666 |
| 2026-09-02 | 39,561 | 283 | 13,524 |
| 2026-09-03 | 60,909 | 303 | 54,894 |
| 2026-09-04 | 82,466 | 304 | 53,274 |
| 2026-09-05 | 84,230 | 351 | 14,410 |
| 2026-09-06 | 112,012 | 564 | 16,819 |
| 2026-09-07 | 146,245 | 600 | 18,267 |
| 2026-09-08 | 285,116 | 782 | 18,906 |
| 2026-09-09 | 578,971 | 800 | 17,167 |
| 2026-09-10 | 615,277 | 1,034 | 17,518 |
| 2026-09-11 | 431,690 | 1,125 | 17,272 |
| 2026-09-12 | 228,283 | 985 | 16,366 |
| 2026-09-13 | 268,596 | 1,027 | 16,666 |
| 2026-09-14 | 235,184 | 1,097 | 17,285 |
| 2026-09-15 | 172,647 | 1,035 | 17,388 |
| 2026-09-16 | 123,854 | 1,017 | 62,100 |
| 2026-09-17 | 101,272 | 976 | 35,609 |
| 2026-09-18 | 114,201 | 918 | 15,490 |
| 2026-09-19 | 137,779 | 897 | 15,184 |
| 2026-09-20 | 132,306 | 1,006 | 16,924 |
| 2026-09-21 | 119,592 | 991 | 38,563 |
| 2026-09-22 | 111,731 | 981 | 38,209 |
| 2026-09-23 | 49,845 | 543 | 12,727 |
| 2026-09-30 | 27,238 | 454 | 6,499 |
| 2026-10-01 | 83,038 | 574 | 13,512 |
| 2026-10-02 | 54,285 | 480 | 11,032 |
Hour of day (UTC)
Interactions by emulated protocol
| Protocol | Interactions | Sources |
|---|---|---|
| vnc | 3,851,508 | 777 |
| ssh | 357,407 | 3,814 |
| mysql | 198,180 | 121 |
| telnet | 31,275 | 1,289 |
| redis | 8,641 | 351 |
| http | 3,404 | 535 |
| ftp | 2,077 | 97 |
| sip | 1,502 | 195 |
| snmp | 858 | 182 |
| tftp | 119 | 103 |
| git | 2 | 2 |
Most-targeted ports (emulated services)
| Port | Protocol | Interactions |
|---|---|---|
| 5900 | VNC | 3,851,508 |
| 22 | SSH | 357,407 |
| 3306 | MYSQL | 198,180 |
| 23 | TELNET | 31,275 |
| 6379 | REDIS | 8,641 |
| 80 | HTTP | 3,404 |
| 21 | FTP | 2,077 |
| 5060 | SIP | 1,502 |
| 161 | SNMP | 858 |
| 69 | TFTP | 119 |
| 9418 | GIT | 2 |
Dropped connection attempts (unemulated ports)
Connection attempts the firewall logged and dropped on ports the sensor doesn't emulate. "egress" rows are traffic leaving the sensor, not attacker traffic.
| Port | Proto | Direction | Hits |
|---|---|---|---|
| 2222 | TCP | input | 6,937 |
| 123 | UDP | egress | 4,306 |
| 3389 | TCP | input | 2,949 |
| 8443 | TCP | input | 2,786 |
| 8000 | TCP | input | 2,012 |
| 554 | TCP | input | 1,637 |
| 53 | TCP | input | 1,212 |
| 53 | UDP | egress | 1,121 |
| 8888 | TCP | input | 1,071 |
| 8081 | TCP | input | 1,006 |
| 25 | TCP | input | 961 |
| 3000 | TCP | input | 919 |
Source countries
| Country | Sources | Hits |
|---|---|---|
| US | 1,794 | 2,380,966 |
| DE | 132 | 892,891 |
| CN | 782 | 208,599 |
| BG | 131 | 193,039 |
| SG | 328 | 165,611 |
| LT | 23 | 148,254 |
| MX | 77 | 61,609 |
| RO | 43 | 48,241 |
| KR | 252 | 38,952 |
| VN | 78 | 32,314 |
| MY | 130 | 26,549 |
| NL | 91 | 22,253 |
| IN | 191 | 17,766 |
| ID | 82 | 17,711 |
| IR | 38 | 16,107 |
Source networks (ASNs)
| ASN | Org | Sources | Hits |
|---|---|---|---|
| AS14061 | DIGITALOCEAN-ASN - DigitalOcean, LLC, US | 180 | 1,436,141 |
| AS51167 | CONTABO - Contabo GmbH, DE | 45 | 797,726 |
| AS398019 | DYNU - Dynu Systems Incorporated, US | 15 | 717,133 |
| AS213790 | LimitedNetwork-AS - Limited Network LTD, GB | 6 | 193,834 |
| AS198364 | BANATSYNC-SRL - BANATSYNC SRL, RO | 66 | 156,829 |
| AS45090 | TENCENT-NET-AP - Shenzhen Tencent Computer Systems Company Limited, CN | 75 | 92,765 |
| AS45102 | ALIBABA-CN-NET - Alibaba (US) Technology Co., Ltd., CN | 137 | 79,203 |
| AS36352 | AS-COLOCROSSING - HostPapa, US | 55 | 74,082 |
| AS37963 | ALIBABA-CN-NET - Hangzhou Alibaba Advertising Co.,Ltd., CN | 88 | 71,917 |
| AS132203 | TENCENT-NET-AP-CN - Tencent Building, Kejizhongyi Avenue, CN | 176 | 63,994 |
| AS22884 | AS22884 - TOTAL PLAY TELECOMUNICACIONES, S.A.P.I. DE C.V., MX | 4 | 61,130 |
| AS197170 | TECHTIES-AS - TechTies Inc., SC | 58 | 45,059 |
| AS48090 | DMZHOST - TECHOFF SRV LIMITED, GB | 16 | 26,397 |
| AS16276 | OVH - OVH SAS, FR | 43 | 21,621 |
| AS55720 | GIGABIT-MY - Gigabit Hosting Sdn Bhd, MY | 20 | 21,172 |
Top source IPs
| Source IP | ASN | Org | Country | Hits | Last seen (UTC) |
|---|---|---|---|---|---|
| 77.90.185.30 | AS213790 | LimitedNetwork-AS - Limited Network LTD, GB | DE | 164,625 | 2026-10-02 20:21:22 |
| 67.205.171.77 | AS14061 | DIGITALOCEAN-ASN - DigitalOcean, LLC, US | US | 161,382 | 2026-09-23 08:09:56 |
| 129.212.183.98 | AS14061 | DIGITALOCEAN-ASN - DigitalOcean, LLC, US | US | 160,784 | 2026-09-23 08:10:13 |
| 159.223.184.166 | AS14061 | DIGITALOCEAN-ASN - DigitalOcean, LLC, US | US | 90,553 | 2026-10-02 21:08:33 |
| 165.227.204.236 | AS14061 | DIGITALOCEAN-ASN - DigitalOcean, LLC, US | US | 82,531 | 2026-09-09 14:47:17 |
| 159.89.225.170 | AS14061 | DIGITALOCEAN-ASN - DigitalOcean, LLC, US | US | 82,393 | 2026-09-09 14:48:04 |
| 159.89.228.57 | AS14061 | DIGITALOCEAN-ASN - DigitalOcean, LLC, US | US | 81,188 | 2026-09-13 09:40:50 |
| 192.241.141.178 | AS14061 | DIGITALOCEAN-ASN - DigitalOcean, LLC, US | US | 77,935 | 2026-10-02 21:09:45 |
| 64.23.175.24 | AS14061 | DIGITALOCEAN-ASN - DigitalOcean, LLC, US | US | 64,519 | 2026-09-23 08:10:12 |
| 129.212.181.73 | AS14061 | DIGITALOCEAN-ASN - DigitalOcean, LLC, US | US | 61,010 | 2026-09-21 13:04:08 |
| 187.191.2.214 | AS22884 | AS22884 - TOTAL PLAY TELECOMUNICACIONES, S.A.P.I. DE C.V., MX | MX | 60,950 | 2026-09-12 22:49:53 |
| 207.174.1.228 | AS398019 | DYNU - Dynu Systems Incorporated, US | US | 58,871 | 2026-09-11 17:06:29 |
| 140.235.18.166 | AS398019 | DYNU - Dynu Systems Incorporated, US | US | 58,128 | 2026-09-11 17:06:28 |
| 207.174.2.239 | AS398019 | DYNU - Dynu Systems Incorporated, US | US | 57,333 | 2026-09-11 17:06:30 |
| 72.51.57.6 | AS398019 | DYNU - Dynu Systems Incorporated, US | US | 57,098 | 2026-09-11 17:06:28 |
Passive TCP/IP fingerprints (p0f)
OS/stack guesses from each inbound SYN's header shape alone. Counts are per packet; "unrecognized" means p0f had no matching signature.
| OS / stack guess | Packets |
|---|---|
| Linux 2.2.x-3.x | 3,100,244 |
| unrecognized | 1,792,077 |
| Windows 7 or 8 | 762,856 |
| Linux 3.11 and newer | 138,101 |
| Linux 2.2.x-3.x (barebone) | 125,711 |
| Windows NT kernel 5.x | 75,978 |
| Windows NT kernel | 69,003 |
| Linux 3.1-3.10 | 7,872 |
| Linux 2.2.x-3.x (no timestamps) | 7,153 |
| Linux 2.4.x | 1,093 |
| FreeBSD | 711 |
| Mac OS X | 623 |
Data notes
- Interaction timestamps are the attacker-side times recorded by the sensor. Most of the 09-13 to 09-23 counts were ingested in one batch on 09-30, after log shipping was repaired.
- No records exist for 09-24 through 09-29 (sensor offline) or after 10-02 21:10 UTC.
- IOC matching compares sources against an abuse.ch ThreatFox IP list. No sources matched in this snapshot.
- This page is static. Figures were frozen at generation time and will not update.